
technology
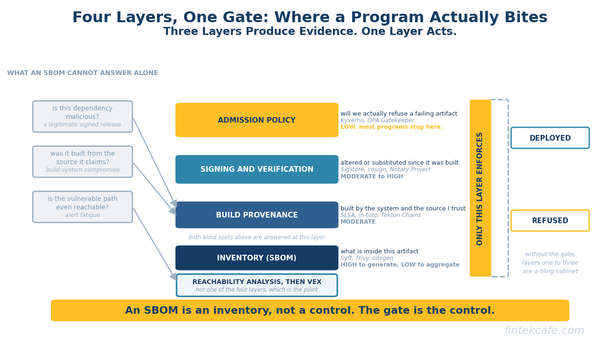
Software Supply Chain Security: What an SBOM Proves and What It Does Not
An SBOM answers one question well and three not at all. What provenance, signing, admission policy, and reachability add, and the order to build them in.
An SBOM answers one question well and three not at all. What provenance, signing, admission policy, and reachability add, and the order to build them in.
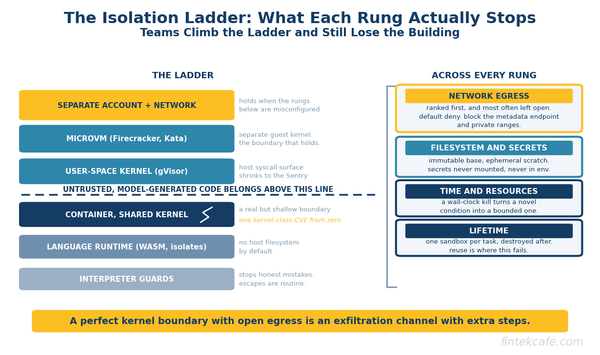
Container, microVM, or separate account: what each agent sandbox rung actually stops, why egress policy matters most, and how to scope agent credentials.
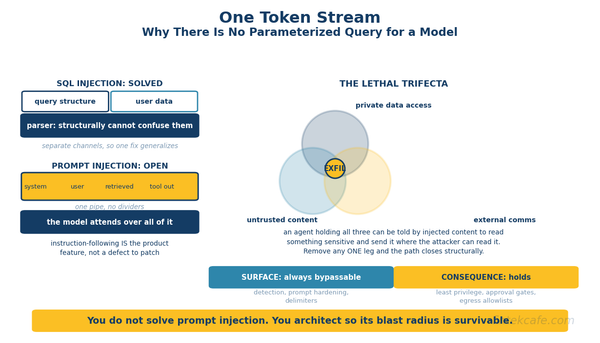
Why prompt injection has no parameterized-query fix, how indirect injection turns agents into attack tools, and the patterns that bound the damage.
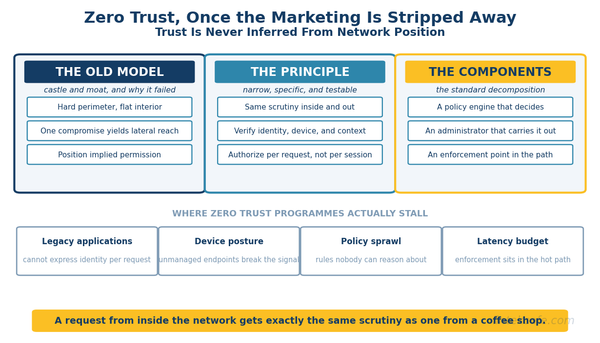
Zero trust explained without the vendor gloss: the real principle, the NIST 800-207 components in plain language, and what a migration actually costs.
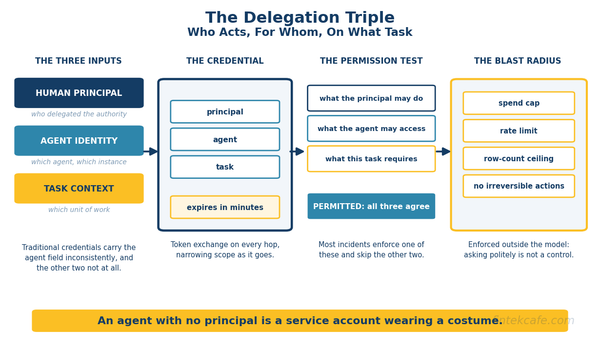
Why API keys break for AI agents, the delegation patterns replacing them, how to scope authorization, and the audit trail attribution requires.
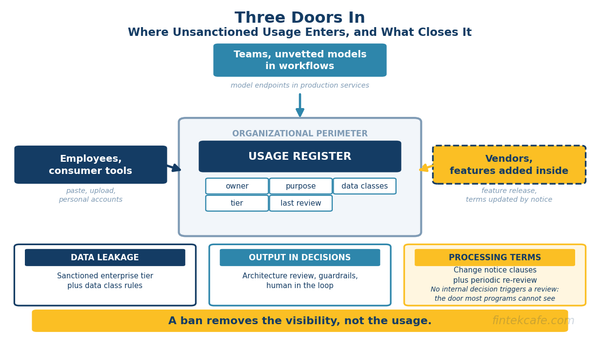
Shadow AI explained: the three exposure classes, why bans fail, how to detect unsanctioned tools, and the tiered governance model that survives contact.
Enterprise browsers are pitched as security tools, but the real prize is control of the last unmanaged surface: every SaaS tab and AI copilot's context.
AI red-teaming explained: the attack taxonomy, how an exercise is structured, what agentic systems add, regulatory pull, cadence, and build-vs-hire.

Guardrails are the control layer between users, your model, and your systems. What they catch, where they sit in the request path, and how to build them.

Shadow AI is a behavioral problem, not a tooling gap. Why bans and CASB underperform, and the governance pattern CISOs should actually fund in 2026.
Confidential computing moved from PowerPoint to procurement in 2025. In 2026 the actual fintech use cases are showing up. A CISO and treasurer playbook.

Deep analysis across the systems, strategies, and economics that shape modern technology.
Premium Members Get: Exclusive deep-dive research · Architecture playbooks · Executive briefings · Full archive access